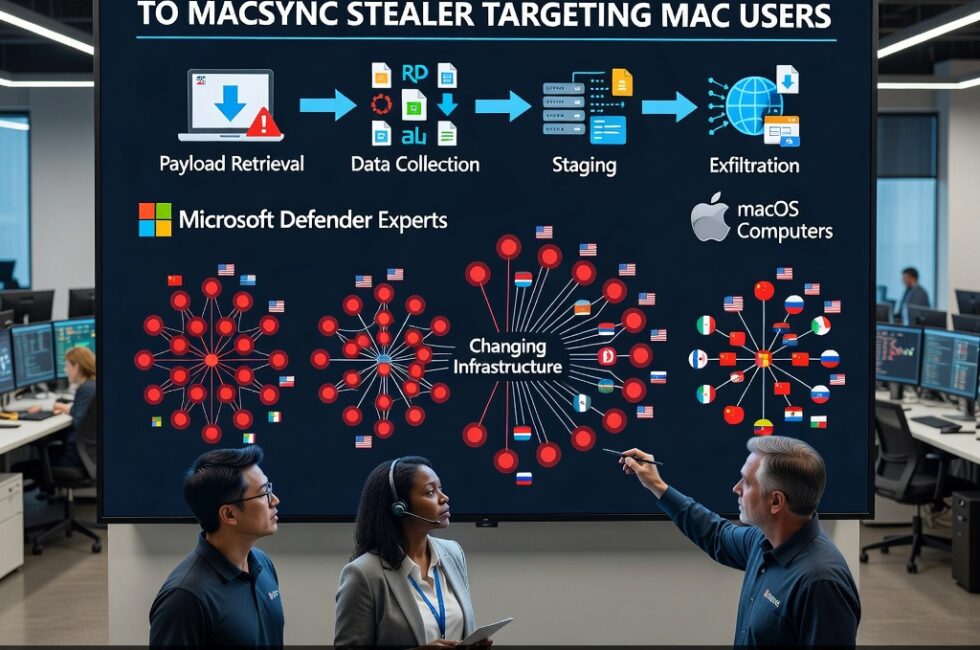
Microsoft Defender Experts have linked more than 30 web domains to MacSync Stealer, a macOS-focused information stealer. They did it by matching the same endpoint and network behaviors even while the operators kept swapping infrastructure. The Hacker News reports that Microsoft traced the malware from payload retrieval through data collection, staging, and exfiltration.
If you use a Mac and figure you are off the menu, you are not. Somebody built a pipeline to pull down a payload, collect data, stage it, and ship it out. Then they kept rotating the domains so the trail would go cold. Microsoft still followed it.
How Microsoft connected 30-plus domains to one Mac stealer
One shady domain does not prove much. Junk sites get stood up every hour. Microsoft said it required multiple endpoint and network behaviors to align before it would treat those sites as part of the same operation.
In plain English, the crew kept changing the front door. The house behind it stayed the same. Recurring behavior on the Mac and on the network let Microsoft Defender Experts tie more than 30 of those doors to MacSync Stealer.
Why rotating domains matter to regular people
Domain rotation is not a party trick. It is how operators try to outrun blocklists, browser warnings, and the security tools that households and small shops actually use. Block yesterday’s address and today’s copy still works.
That is why a cluster of 30-plus related domains is the story, not a trivia item. It is a map of a moving target. Microsoft followed the whole chain, not just one download URL:
- Payload retrieval: the Mac reaches out and pulls down the stealer.
- Data collection: the malware gathers information from the machine.
- Staging: stolen data gets packed up locally before it leaves.
- Exfiltration: that data gets sent out to attacker-controlled infrastructure.
What Mac users should do with this
An information stealer exists to take what is sitting on the computer. You do not need a domain list taped to the monitor. You need to stop treating every Mac prompt like it came from a friend.
- Do not install software from random links, surprise “update” pop-ups, or cracked apps.
- Keep macOS and your browser current. Old holes stay useful longer than people think.
- Treat unexpected permission prompts like a stranger asking for your house keys.
- If you run a small shop on Macs, you want tools that can see endpoint behavior and outbound traffic. Domain lists go stale. Repeated behavior does not.
- If a Mac starts acting off, assume logins and saved sessions may already be in play. Change the important passwords from a clean machine.
Microsoft connecting more than 30 domains does not mean this is over. It means the operators were organized enough to keep rebuilding the on-ramp, and someone finally mapped the pattern. Regular Mac users do not need the jargon. They need to quit trusting every download that shows up on the screen.
Primary Source: https://thehackernews.com/2026/08/microsoft-links-30-rotating-domains-to.html